Source: Microsoft
A security researcher has found several vulnerabilities in the popular open-source Horde web email software that allow hackers to near-invisibly steal the contents of a victim’s inbox.
Horde is one of the most popular free and open-source web email systems available. It’s built and maintained by a core team of developers, with contributions from the wider open-source community. It’s used by universities, libraries, and many web hosting providers as the default email client.
Numan Ozdemir disclosed his vulnerabilities to Horde in May. An attacker can scrape and download a victim’s entire inbox by tricking them into clicking a malicious link in an email.
Once clicked, the inbox is downloaded to the attacker’s server.
But the researcher did not hear back from the Horde community. Security researchers typically give organizations three months to fix flaws before they are publicly disclosed.
NIST, the government department that maintains the national vulnerability database, said this week that the flaws pose a “high” security risk to users.
Ozdemir said some — though not all — of the vulnerabilities were recently fixed in the latest Horde webmail version. But the Horde community has not publicly acknowledged the vulnerability — or that users of earlier versions of the webmail are still vulnerable.
“It is really very easy to steal people’s email,” he told TechCrunch.
His bug report filed with Horde remains open at the time of writing. We emailed Horde several times, but did not hear back.
Hackers can steal the contents of Horde webmail inboxes with one click
Source: Microsoft
An American giant may have figured out a way to simplify the tedious procedure of issuing driver’s licenses. And an early sneak peek of this solution is now live in parts of India.
Hundreds of people who have taken the driver’s license test in Dehradun, the capital of Indian state Uttarakhand near the Himalayan foothills, in recent weeks haven’t had to sit next to an instructor.
Instead, their cars were affixed with a smartphone that was running HAMS, an AI project developed by Microsoft Research team. HAMS uses a smartphone’s front and rear cameras and other sensors to monitor the driver (their gaze), and the road ahead of them. Microsoft Research team said for driver tests, they customized HAMS to enable precise tracking of a vehicle’s trajectory during test manoeuvres such as parallel parking or negotiating a roundabout.
This AI technology can determine whether the driver performed any action — such as stopping in the middle of a test or course correcting by rolling forward or backward more times than they were allowed — during the test, the team said. Additionally, it also checks things like whether a driver scanned their mirrors before changing the lane.
Shri Shailesh Bagauli, IAS, Secretary of Government of Uttarakhand, said the deployment of HAMS-based driver license testing at the Dehradun RTO is a “significant step towards the Transport Department’s goal of providing efficient, world-leading services to the citizens of Uttarakhand. We are proud to be among the pioneers of the application of AI to enhance road safety.”
HAMS, short for Harnessing AutoMobiles for Safety, was originally developed to monitor drivers and their driving to improve road safety. “Driver training and testing are foundational to this goal, and so the project naturally veered in the direction of helping evaluate drivers during their driving test,” the team said.
Automation is slowly making its way to driver testing across the world, but they still require deployment of extensive infrastructure such as pole-mounted video cameras along the test track. Microsoft’s team said HAMS can bring down the cost of automation while improving test coverage by including a view within the vehicle.
Some surveys (PDF) have shown that a significant number of applicants don’t even show up to give a test to obtain their license because of the “burden” they would have to go through. “Automation using HAMS technology can not only help relieve evaluators of the burden but also make the process objective and transparent for candidates,” says Venkat Padmanabhan, Deputy Managing Director, Microsoft Research India, who started the HAMS project in 2016.
The test venue of this project should not come as a surprise. American technology companies are increasingly expanding their presence in India, one of the last great growth markets with several unique local challenges.
Microsoft, Google, and Amazon have used India a a test bed to build solutions for the local market, some of which eventually make it to other countries. Microsoft has previously developed tools to help farmers in India increase their crop yields and worked with hospitals to prevent avoidable blindness. Last year, the company partnered with Apollo Hospitalls to create an AI-powered API customized to predict risk of heart diseases in India.
Last year, the company also worked with cricket legend Anil Kumble to develop a tracking device that helps youngsters analyze their batting performance. Microsoft has also tied up with insurance firm ICICI Lombard to help it process customers’ repair claims and renew lapsed policies using an AI system.
Google has also developed a range of services and tools for India. The company last year launched a tool to help publishers easily bring stories written in local languages to the web. This year, the Android-maker unveiled improvements it has made to its flood prediction tool. And of course, several popular apps such as YouTube Go, and Google Station started as India-only services.
Driving license tests just got smarter in India with Microsoft’s AI project
Source: Microsoft
Microsoft-owned Github has removed the APK of an app for organizing political protests in the autonomous community of Catalonia — acting on a takedown request from Spain’s military police (aka the Guardia Civil).
As we reported earlier this month supporters of independence for Catalonia have regrouped under a new banner — calling itself Tsunami Democràtic — with the aim of rebooting the political movement and campaigning for self-determination by mobilizing street protests and peaceful civil disobedience.
The group has also been developing bespoke technology tools to coordinate protest action. It’s one of these tools, the Tsunami Democràtic app, which was being hosted as an APK on Github and has now been taken down.
The app registers supporters of independence by asking them to communicate their availability and resources for taking part in local protest actions across Catalonia. Users are also asked to register for protest actions and check-in when they get there — at which point the app asks them to abide by a promise of non-violence (see point 3 in this sample screengrab):
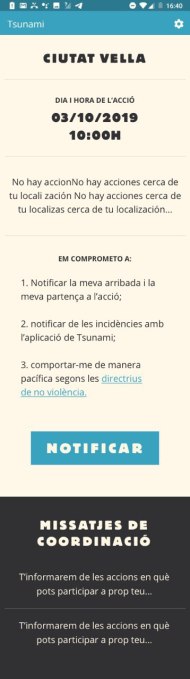
Users of the app see only upcoming protests relevant to their location and availability — making it different to the one-to-many broadcasts that Tsunami Democràtic also puts out via its channel on the Telegram messaging app.
Essentially, it’s a decentalized tool for mobilizing smaller, localized protest actions vs the largest demos which continue to be organized via Telegram broadcasts (such as a mass blockade of Barcelona airport, earlier this month).
A source with knowledge of Tsunami Democràtic previously told us the sorts of protests intended to be coordinated via the app could include actions such as go-slows to disrupt traffic on local roads and fake shopping sprees in supermarkets, with protestors abandoning carts filled with products in the store.
In a section of Github’s site detailing government takedowns the request from the Spanish state to remove the Tsunami Democràtic app sits alongside folders containing historical takedown requests from China and Russia.
“There is an ongoing investigation being carried out by the National High Court where the movement Tsunami Democràtic has been confirmed as a criminal organization driving people to commit terrorist attacks. Tsunami Democràtic’s main goal is coordinating these riots and terrorist actions by using any possible mean,” Spain’s military police write in the letter sent to Github.
We’ve reached out to Microsoft for comment on Github’s decision to remove the app APK.
In a note about government takedowns on Github’s website it writes:
From time to time, GitHub receives requests from governments to remove content that has been declared unlawful in their local jurisdiction. Although we may not always agree with those laws, we may need to block content if we receive a valid request from a government official so that our users in that jurisdiction may continue to have access to GitHub to collaborate and build software.
“GitHub does not endorse or adopt any assertion contained in the following notices,” it adds in a further caveat on the page.
The trigger for the latest wave of street demonstrations in Catalonia were lengthy jail sentences handed down to a number of Catalan political and cultural leaders by Spain’s Supreme Court earlier this month.
These were people involved in organizing an illegal independence referendum two years ago. The majority of these Catalan leaders were convicted for sedition. None were found guilty of the more serious charge of rebellion — but sentences ran as long as 13 years nonetheless.
This month Spanish judges also reissued a European arrest warrant seeking to extradite the former leader of the Catalan government, Carles Puigdemont, from Brussels to Spain to face trial. Last year a court in Germany refused his extradition to Spain on charges of rebellion or sedition — only allowing it on lesser grounds of misuse of public funds. A charge which Spain did not pursue.
Puigdemont fled Catalonia in the wake of the failed 2017 independence bid and has remained living in exile in Brussels. He has also since been elected as an MEP but has been unable to take up his seat in the EU parliament after the Spanish state moved to block him from being recognized as a parliamentarian.
Shortly after the latest wave of pro-independence demonstrations took off in Catalonia the Tsunami Democràtic movement’s website was taken offline — also as a result of a takedown request by the Spanish state.
The website remains offline at the time of writing.
While the Tsunami Democràtic app could be accused of encouraging disruption, the charge of “terrorism” is clearly overblown. Unless your definition of terrorism extends to harnessing the power of peaceful civil resistance to generate momentum for political change.
And while there has been unrest on the streets of Barcelona and other Catalan towns and cities this month, with fires being lit and projectiles thrown at police, there are conflicting reports about what has triggered these clashes between police and protestors — including criticism of the police response as overly aggressive vs what has been, in the main, large but peaceful crowds of pro-democracy demonstrators.
The police response on the day of the 2017 referendum was also widely condemned as violently disproportionate, with scenes of riot gear clad police officers beating up people as they tried to cast a vote.
Local press in Catalonia has reported the European Commission response to Spain’s takedown of the Tsunami Democràtic website — saying the pan-EU body said Spain has a responsibility to find “the right balance between guaranteeing freedom of expression and upholding public order and ensuring security, as well as protecting [citizens] from illegal content”.
Asked what impact the Github takedown of the Tsunami Democràtic app’s APK will have on the app, a source with knowledge of the movement suggested very little — pointing out that the APK is now being hosted on Telegram.
Similarly, the content that was available on the movement’s website is being posted to its 380,000+ subscribers on Telegram — a messaging platform that’s itself been targeted for blocks by authoritarian states in various locations around the world. (Though not, so far, in Spain.)
Another protest support tool that’s been in the works in Catalonia — a live-map for crowdsourcing information about street protests which looks similar to the HKlive.maps app used by pro-democracy campaigners in Hong Kong — is still in testing but expected to launch soon, per the source.
Github removes Tsunami Democràtic’s APK after a takedown order from Spain
Source: Microsoft
Slack created a new solution for workplace communication, one copied by many, even Microsoft. But the product, which is meant to help individuals and businesses collaborate, has been critiqued for sending too many notifications, with some claiming it’s sabotaged workplace productivity.
Quill, a startup led by Ludwig Pettersson, Stripe’s former creative director and design aficionado, claims to offer “meaningful conversations, without disturbing your team.” The company has raised a $2 million seed round led by Sam Altman with participation from General Catalyst, followed by a $12.5 million Series A at a $62.5 million valuation led by Index Ventures partner and former Slack board observer Sarah Cannon, TechCrunch has learned.
Quill and Cannon declined to comment.
The company, based in San Francisco, has created a no-frills messaging product. Still in beta, Quill plans to encourage fewer, more focused conversations with a heavy emphasis on threads, sources tell TechCrunch . The product is less of a firehose than Slack, says former Y Combinator president Altman, where one can get stuck for extended periods of time filtering through direct messages, threads and channels.
“It’s relentlessly focused on increasing the bandwidth and efficiency of communication,” Altman tells TechCrunch. “The product technically works super well–it surfaces the right information in the feed and it’s pretty intelligent about how it brings the right people into conversations.”
Pettersson previously worked with Altman at his current venture, OpenAI, a research-driven business focused on development that steers artificial intelligence in a “friendlier” direction. Pettersson was a member of the company’s technical staff in 2016 and 2017, creating OpenAI’s initial design.
Index Ventures, for its part, appears to be doubling down on the growing workplace communications software category. The firm first invested in Slack, which completed its highly-anticipated direct listing earlier this year, in 2015. Slack went on to raise hundred millions more, reaching a valuation of over $7 billion in 2018.
Since going public, Slack has struggled to find its footing on the public markets, in large part due to the growing threat of Microsoft Teams, the software giant’s Slack-like product that debuted in 2016. Quickly, Microsoft has gobbled up market share, offering convenient product packages including beloved tools used by most businesses. As of July, Teams had 13 million daily active users and the title of Microsoft’s fastest-growing application in its history. Slack reported 12 million daily active users earlier this month.
Startups like Quill pose a threat to Slack, too. It created the playbook for workplace chat software and proved the massive appetite for such tools; companies are bound to iterate on the model for years to come.
Quill is also backed by OpenAI’s chairman and chief technology officer Greg Brockman and Elad Gil, a former Twitter executive and co-founder of Color Genomics.
Slack investor Index Ventures backs Slack competitor Quill
Source: Microsoft
Amazon, Microsoft and Google are often referred to as the Big 3 in the cloud infrastructure market, and if you had any doubt about the growth potential of the cloud, take a look at this quarter’s eye-popping revenue numbers from these three companies, which reached almost $22 billion this earnings’s season.
Before we get into each company’s specific numbers, it’s important to note that it’s difficult to get a firm grip on what the cloud numbers actually mean and what each company includes in that cloud revenue category. What’s more, this quarter Google didn’t even report specific cloud revenue, so we are left to rely on comments from July.
It’s also important to note that we are talking about the cloud infrastructure, not SaaS revenue, so Microsoft earned additional money from their SaaS business, but Google combines SaaS and infrastructure into a single number.
That said, we have a rough idea and we know the market is growing. Consider that based on last year’s earnings reports that revenue has grown from around $16 billion to around $22 billion in just one year for these Big 3. In fact, Synergy Research reports that the entire market is on $100 billion run rate for the first time this month.
AWS
Photo: Budrul Chukrut/SOPA Images/LightRocket via Getty Images
Let’s start with AWS. They have the purest numbers when it comes to the cloud market, and they have the largest chunk of marketshare by far. Most analysts peg them at around 33 percent or so, well ahead of any other player on the market.
Amazon reported revenue of almost $9 billion this month, putting it on a run rate of almost $36 billion. Not bad for a side business for the main Amazon e-commerce site. Amazon’s overall growth rate dropped from around 45% to around 35%, but as John Dinsdale from Synergy Research points out, that’s still a good rate, and it becomes much harder to sustain large growth numbers the bigger you get.
Microsoft
Photo: Budrul Chukrut/SOPA Images/LightRocket via Getty Images
Microsoft had a good week. It reported Intelligent Cloud earnings of around $11 billion, and it was awarded the Pentagon’s $10 billion, decade long JEDI cloud contract. The company is in second place in terms of marketshare with around 16%.
Like Amazon, Microsoft saw its cloud growth slow a bit, down to 59% compared with 76% a year ago, but it faces a similar challenge to Amazon, even though it has half the marketshare. It’s scaling so quickly that it can’t really maintain that growth pace it’s been on, according to Dinsdale. “To be at the scale that Azure has achieved and to be still growing at around 60% per year is impressive. Sure the growth rate is nudging down but that is entirely to be expected for a business that has rapidly grown,” he told TechCrunch.
It’s important to point out that Intelligent Cloud includes much more than Azure including SQL Server, Windows Server, Visual Studio, consulting and support.
Google
Photo: Budrul Chukrut/SOPA Images/LightRocket via Getty Images
Finally we have Google. It has far less marketshare than Amazon or Microsoft, somewhere around 8%, still in the single digits, but growing fast. The company brought on former Oracle executive Thomas Kurian to replace Diane Greene at the end of last year to help drive growth at the cloud division.
In July, at the company’s earnings report, Google CEO Sundar Pichai reported that the company was on an $8 billion run rate, or $2 billion a quarter. To put that into perspective, the company’s cloud revenue had doubled in 18 months. It’s important to note however that figure includes both Google’s infrastructure services and its commercial SaaS tools like G Suite. It probably ticked up this week, but Google wasn’t sharing specific numbers this time.
While it’s always been difficult to compare cloud numbers, we have a good sense of how each of the Big 3 is doing overall. One thing is clear: this is not a fixed pie. The cloud market is still growing rapidly, and all three companies are taking advantage.
Big 3 cloud infrastructure earnings reach almost B this quarter
Source: Microsoft
It’s a year since the European Commission got a bunch of adtech giants together to spill ink on a voluntary Code of Practice to do something — albeit, nothing very quantifiable — as a first step to stop the spread of disinformation online.
Its latest report card on this voluntary effort sums to the platforms could do better.
The Commission said the same in January. And will doubtless say it again. Unless or until regulators grasp the nettle of online business models that profit by maximizing engagement. As the saying goes, lies fly while the truth comes stumbling after. So attempts to shrink disinformation without fixing the economic incentives to spread BS in the first place are mostly dealing in cosmetic tweaks and optics.
Signatories to the Commission’s EU Code of Practice on Disinformation are: Facebook, Google, Twitter, Mozilla, Microsoft and several trade associations representing online platforms, the advertising industry, and advertisers — including the Internet Advertising Bureau (IAB) and World Federation of Advertisers (WFA).
In a press release assessing today’s annual reports, compiled by signatories, the Commission expresses disappointment that no other Internet platforms or advertising companies have signed up since Microsoft joined as a late addition to the Code this year.
“We commend the commitment of the online platforms to become more transparent about their policies and to establish closer cooperation with researchers, fact-checkers and Member States. However, progress varies a lot between signatories and the reports provide little insight on the actual impact of the self-regulatory measures taken over the past year as well as mechanisms for independent scrutiny,” write commissioners Věra Jourová, Julian King, and Mariya Gabriel said in a joint statement. [emphasis ours]
“While the 2019 European Parliament elections in May were clearly not free from disinformation, the actions and the monthly reporting ahead of the elections contributed to limiting the space for interference and improving the integrity of services, to disrupting economic incentives for disinformation, and to ensuring greater transparency of political and issue-based advertising. Still, large-scale automated propaganda and disinformation persist and there is more work to be done under all areas of the Code. We cannot accept this as a new normal,” they add.
The risk, of course, is that the Commission’s limp-wristed code risks rapidly cementing a milky jelly of self-regulation in the fuzzy zone of disinformation as the new normal, as we warned when the Code launched last year.
The Commission continues to leave the door open (a crack) to doing something platforms can’t (mostly) ignore — i.e. actual regulation — saying it’s assessment of the effectiveness of the Code remains ongoing.
But that’s just a dangled stick. At this transitionary point between outgoing and incoming Commissions, it seems content to stay in a ‘must do better’ holding pattern. (Or: “It’s what the Commission says when it has other priorities,” as one source inside the institution put it.)
A comprehensive assessment of how the Code is working is slated as coming in early 2020 — i.e. after the new Commission has taken up its mandate. So, yes, that’s the sound of the can being kicked a few more months on.
Summing up its main findings from signatories’ self-marked ‘progress’ reports, the outgoing Commission says they have reported improved transparency between themselves vs a year ago on discussing their respective policies against disinformation.
But it flags poor progress on implementing commitments to empower consumers and the research community.
“The provision of data and search tools is still episodic and arbitrary and does not respond to the needs of researchers for independent scrutiny,” it warns.
This is ironically an issue that one of the signatories, Mozilla, has been an active critic of others over — including Facebook, whose political ad API it reviewed damningly this year, finding it not fit for purpose and “designed in ways that hinders the important work of researchers, who inform the public and policymakers about the nature and consequences of misinformation”. So, er, ouch.
The Commission is also critical of what it says are “significant” variations in the scope of actions undertaken by platforms to implement “commitments” under the Code, noting also differences in implementation of platform policy; cooperation with stakeholders; and sensitivity to electoral contexts persist across Member States; as well as differences in EU-specific metrics provided.
But given the Code only ever asked for fairly vague action in some pretty broad areas, without prescribing exactly what platforms were committing themselves to doing, nor setting benchmarks for action to be measured against, inconsistency and variety is really what you’d expect. That and the can being kicked down the road.
The Code did extract one quasi-firm commitment from signatories — on the issue of bot detection and identification — by getting platforms to promise to “establish clear marking systems and rules for bots to ensure their activities cannot be confused with human interactions”.
A year later it’s hard to see clear sign of progress on that goal. Although platforms might argue that what they claim is increased effort toward catching and killing malicious bot accounts before they have a chance to spread any fakes is where most of their sweat is going on that front.
Twitter’s annual report, for instance, talks about what it’s doing to fight “spam and malicious automation strategically and at scale” on its platform — saying its focus is “increasingly on proactively identifying problematic accounts and behaviour rather than waiting until we receive a report”; after which it says it aims to “challenge… accounts engaging in spammy or manipulative behavior before users are exposed to misleading, inauthentic, or distracting content”.
So, in other words, if Twitter does this perfectly — and catches every malicious bot before it has a chance to tweet — it might plausibly argue that bot labels are redundant. Though it’s clearly not in a position to claim it’s won the spam/malicious bot war yet. Ergo, its users remain at risk of consuming inauthentic tweets that aren’t clearly labeled as such (or even as ‘potentially suspect’ by Twitter). Presumably because these are the accounts that continue slipping under its bot-detection radar.
There’s also nothing in Twitter’s report about it labelling even (non-malicious) bot accounts as bots — for the purpose of preventing accidental confusion (after all satire misinterpreted as truth can also result in disinformation). And this despite the company suggesting a year ago that it was toying with adding contextual labels to bot accounts, at least where it could detect them.
In the event it’s resisted adding any more badges to accounts. While an internal reform of its verification policy for verified account badges was put on pause last year.
Facebook’s report also only makes a passing mention of bots, under a section sub-headed “spam” — where it writes circularly: “Content actioned for spam has increased considerably, since we found and took action on more content that goes against our standards.”
It includes some data-points to back up this claim of more spam squashed — citing a May 2019 Community Standards Enforcement report — where it states that in Q4 2018 and Q1 2019 it acted on 1.8 billion pieces of spam in each of the quarters vs 737 million in Q4 2017; 836 million in Q1 2018; 957 million in Q2 2018; and 1.2 billion in Q3 2018.
Though it’s lagging on publishing more up-to-date spam data now, noting in the report submitted to the EC that: “Updated spam metrics are expected to be available in November 2019 for Q2 and Q3 2019″ — i.e. conveniently late for inclusion in this report.
Facebook’s report notes ongoing efforts to put contextual labels on certain types of suspect/partisan content, such as labelling photos and videos which have been independently fact-checked as misleading; labelling state-controlled media; and labelling political ads.
Labelling bots is not discussed in the report — presumably because Facebook prefers to focus attention on self-defined spam-removal metrics vs muddying the water with discussion of how much suspect activity it continues to host on its platform, either through incompetence, lack of resources or because it’s politically expedient for its business to do so.
Labelling all these bots would mean Facebook signposting inconsistencies in how it applies its own policies –in a way that might foreground its own political bias. And there’s no self-regulatory mechanism under the sun that will make Facebook fess up to such double-standards.
For now, the Code’s requirement for signatories to publish an annual report on what they’re doing to tackle disinformation looks to be the biggest win so far. Albeit, it’s very loosely bound self-reporting. While some of these ‘reports’ don’t even run to a full page of A4-text — so set your expectations accordingly.
The Commission has published all the reports here. It has also produced its own summary and assessment of them (here).
“Overall, the reporting would benefit from more detailed and qualitative insights in some areas and from further big-picture context, such as trends,” it writes. “In addition, the metrics provided so far are mainly output indicators rather than impact indicators.”
Of the Code generally — as a “self-regulatory standard” — the Commission argues it has “provided an opportunity for greater transparency into the platforms’ policies on disinformation as well as a framework for structured dialogue to monitor, improve and effectively implement those policies”, adding: “This represents progress over the situation prevailing before the Code’s entry into force, while further serious steps by individual signatories and the community as a whole are still necessary.”
Tech giants still not doing enough to fight fakes, says European Commission
Source: Microsoft
The DoD JEDI contract saga came to a thrilling conclusion on Friday afternoon, appropriately enough, with one final plot twist. The presumptive favorite, Amazon did not win, stunning many, including likely the company itself. In the end, Microsoft took home the $10 billion prize.
This contract was filled with drama from the beginning, given the amount of money involved, the length of the contract, the winner-take-all nature of the deal — and the politics. We can’t forget the politics. This was Washington after all and Jeff Bezos does own the Washington Post.
Then there was Oracle’s fury throughout the procurement process. The president got involved in August. The current defense secretary recused himself on Wednesday, two days before the decision came down. It was all just so much drama, even the final decision itself, handed down late Friday afternoon, but it’s unclear if this is the end or just another twist in this ongoing tale.
Some perspective on $10 billion
Before we get too crazy about Microsoft getting a $10 billion, 10 year contract, consider that Amazon earned $9 billion last quarter alone in cloud revenue. Microsoft reported $33 billion last quarter in total revenue. It reported around $11 billion in cloud revenue. Synergy Research pegs the current cloud infrastructure market at well over $100 billion annually (and growing).
What we have here is a contract that’s worth a billion a year. What’s more, it’s possible it might not even be worth that much if the government uses one of its out clauses. The deal is actually initially guaranteed for just two years. Then there are a couple of three-year options, with a final two-year option at the end if gets that far.
The DOD recognized that with the unique nature of this contract, going with a single vendor, it wanted to keep its options open should the tech world shift suddenly under its feet. It didn’t want to be inextricably tied to one company for a decade if that company was suddenly disrupted by someone else. Given the shifting sands of technology, that part of the strategy was a wise one.
Where the value lies
If value of this deal was not the contract itself, it begs the question, why did everyone want it so badly? The $10 billion JEDI deal was simply a point of entree. If you could modernize the DoD’s infrastructure, the argument goes, chances are you could do the same for other areas of the government. It could open the door for Microsoft for a much more lucrative government cloud business.
But it’s not as though Microsoft didn’t already have a lucrative cloud business. In 2016, for example, the company signed a deal worth almost a billion dollars to help move the entire department to Windows 10. Amazon too, has had its share of government contracts, famously landing the $600 million to build the CIA’s private cloud.
But given all the attention to this deal, it always felt a little different from your standard government contract. Just the fact the DoD used a Star Wars reference for the project acronym drew more attention to the project from the start. Therefore, there was some prestige for the winner of this deal, and Microsoft gets bragging rights this morning, while Amazon is left to ponder what the heck happened. As for other companies like Oracle, who knows how they’re feeling about this outcome.
Hell hath no fury like Oracle scorned
Ah yes Oracle; this tale would not be complete without discussing the rage of Oracle throughout the JEDI RFP process. Even before the RFP process started, they were complaining about the procurement process. Co-CEO Safra Catz had dinner with the president to complain that contract process wasn’t fair (not fair!). Then it tried complaining to the Government Accountability Office. They found no issue with the process.
They went to court. The judge dismissed their claims that involved both the procurement process and that a former Amazon employee, who was hired by DoD, was involved in the process of creating the RFP. They claimed that the former employee was proof that the deal was tilted toward Amazon. The judge disagreed and dismissed their complaints.
What Oracle could never admit, was that it simply didn’t have the same cloud chops that Microsoft and Amazon, the two finalists, had. It couldn’t be that they were late to the cloud or had a fraction of the market share that Amazon and Microsoft had. It had to be the process or that someone was boxing them out.
What Microsoft brings to the table
Outside of the politics of this decision (which we will get to shortly), Microsoft brought some experience and tooling the table that certainly gave it some advantage in the selection process. Until we see the reasons for the selections, it’s hard to know exactly why DoD chose Microsoft, but we know a few things.
First of all there are the existing contracts with DoD, including the aforementioned Windows 10 contract and a five year $1.76 billion contract with DoD Intelligence to provide “innovative enterprise services” to the DoD.
Then there is Azure Stack, a portable private cloud stack that the military could stand up anywhere. It could have great utility for missions in the field when communicating with a cloud server could be problematic.
Fool if you think it’s over
So that’s that right? The decision has been made and it’s time to move on. Amazon will go home and lick its wounds. Microsoft gets bragging rights and we’re good. Actually, this might not be where it ends at all.
Amazon for instance could point to Jim Mattis’ book where he wrote that the president told the then Defense Secretary to “screw Bezos out of that $10 billion contract.” Mattis says he refused saying he would go by the book, but it certainly leaves the door open to a conflict question.
It’s also worth pointing out that Jeff Bezos owns the Washington Post and the president isn’t exactly in love with that particular publication. In fact, this week, the White House canceled its subscription and encouraged other government agencies to do so as well.
Then there is the matter of current Defense Secretary Mark Espers suddenly recusing himself last Wednesday afternoon based on a minor point that one of his adult children works at IBM (in a non-cloud consulting job). He claimed he wanted to remove any hint of conflict of interest, but at this point in the process, it was down to Microsoft and Amazon. IBM wasn’t even involved.
If Amazon wanted to protest this decision, it seems it would have much more solid ground to do so than Oracle ever had.
The bottom line is a decision has been made, at least for now, but this process has been rife with controversy from the start, just by the design of the project, so it wouldn’t be surprising to see Amazon take some protest action of its own. It seems oddly appropriate.
Even after Microsoft wins, JEDI saga could drag on
Source: Microsoft
The U.S. Department of Defense today announced that Microsoft has won its Joint Enterprise Defense Infrastructure (JEDI) cloud contract, worth up to $10 billion over a period of 10 years. With this, Microsoft will provide infrastructure and platform services for both the Pentagon’s business and mission operations.
“The National Defense Strategy dictates that we must improve the speed and effectiveness with which we develop and deploy modernized technical capabilities to our women and men in uniform,” DOD Chief Information Officer Dana Deasy said in a related announcement. “The DOD Digital Modernization Strategy was created to support this imperative. This award is an important step in execution of the Digital Modernization Strategy.”
Microsoft beat out Amazon in the final round for this lucrative contract after the two cloud giants beat out other competitors like IBM and Oracle in an earlier round. Most pundits considered Amazon to be the frontrunner to win the deal.
The process to get to this point has been anything but uncomplicated, though, with various lawsuits, last-minute recusals and other controversies, with even the president getting involved at one point.
It’ll remain to be seen how Microsoft’s employees will react to this news. Last year, a number of Microsoft employees posted an open letter asking the company not to bid for the contract. More recently, its employees also protested against GitHub’s relatively small $200,000 contract with the U.S. Immigration and Customs Enforcement agency. Against this backdrop, chances are we’ll see similar protests now that the company has won this deal with the Pentagon.
In a victory over Amazon, Microsoft wins B Pentagon JEDI cloud contract
Source: Microsoft
Rory O’Driscoll
Contributor
Enterprise software investor
Rory O’Driscoll led
Scale Venture Partners’ investments in Box, DocuSign, ExactTarget, and Omniture, and currently invests in AI-powered business applications and automation technologies.
More posts by this contributor
SaaS has been the motherlode of enterprise software investing for two decades now. Venture investors, entrepreneurs, and Wall Street have all learned to pile on, leading to a shared consensus that cloud investing is “a sure thing.” Nothing is more destructive to investors over the long term than a sure thing, so I began to wonder, “what could cause the wonderful economics of cloud investing to unravel?”
My conclusion is that while the cloud is obviously here to stay, the next five years in cloud investing will neither be the same nor as easy as the last 10. My reason for writing this post is not to be a party pooper, but to provide a context for startups to navigate this potentially harsher environment. This post identifies three different startup strategies, all of which can work even in the more competitive cloud economy that I envisage. More on that below.
Big picture, the summary points are as follows:
First, cloud company valuations are at all-time highs which cannot be justified by improved company operating performance but can explained by 20 years of consistent 30% growth in the cloud software market. This has given investors the comfort to “pay up.”
Second, within the next two to three years, there will be a “growth crunch” as many cloud markets saturate. At that point the Gold Rush will become the Hunger Games, as cloud companies large and small compete against each other for survival.
Third, there will be three winning strategies for a startup when this happens: fight, or compete head on in an existing cloud market; focus, or find those parts of the cloud market where there is still low competition and good growth; fly, which is to build a company based on more than just the move to the cloud.
Fourth, “beyond the cloud” means “assume the cloud” and build on top of that stack using newer technologies and a design approach where instead of the user working for the software, the software works for (or instead of) the user. At Scale, we think of this as building the Intelligent Connected World (ICW).
Let’s walk through the details.
How did we get here?
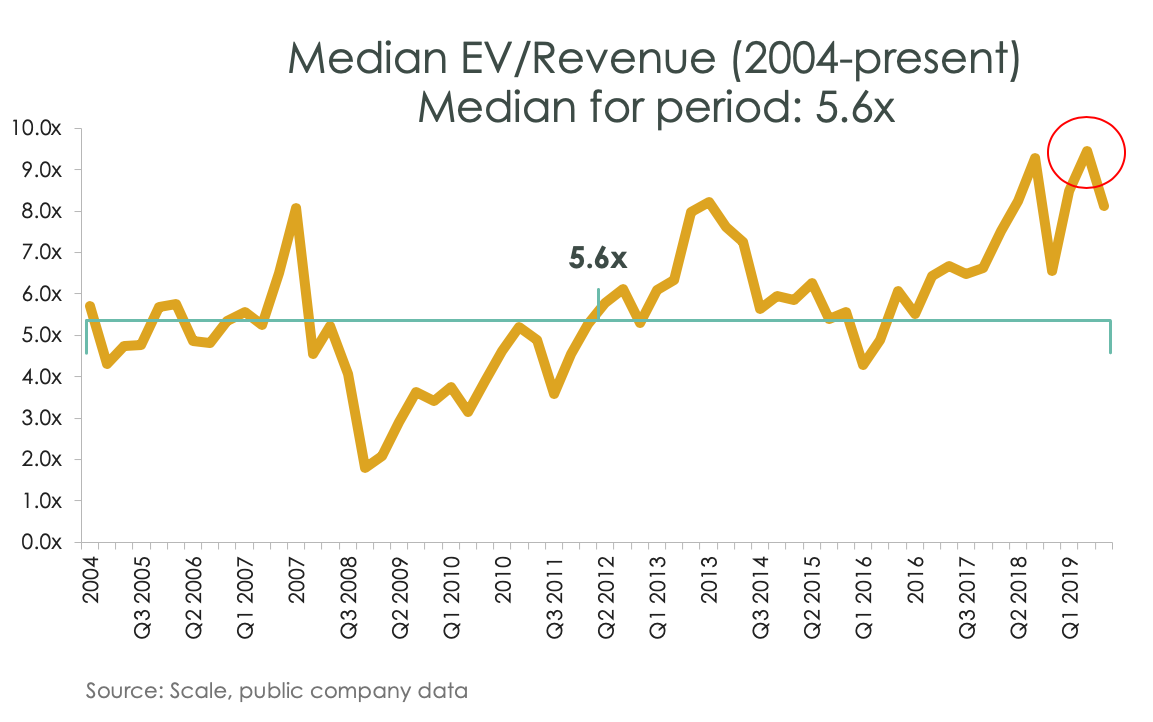
We got here because the cloud model works. It works as a computer architecture, and there is no clear replacement architecture on the horizon. It works for customers by aligning incentives with vendors to keep their software working. And it works – brilliantly – as a financial model. In a world of low growth and low interest rates, SaaS looks like a perpetual motion machine and the valuations show it. Today the median SaaS multiple is 8.5x run rate versus an all-time average of 5.6x. Higher growth companies trade at even loftier multiples of 20x and 30x.
Are cloud companies performing better than ever?
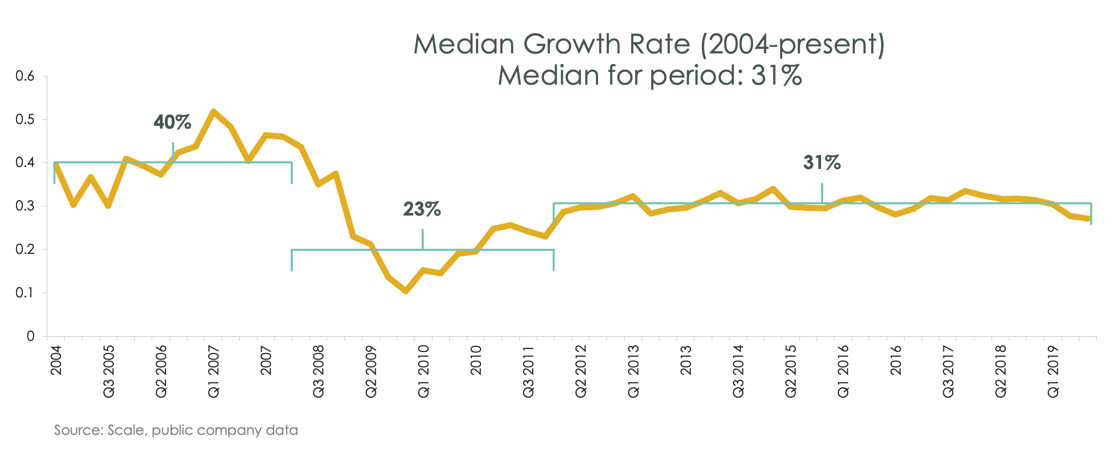
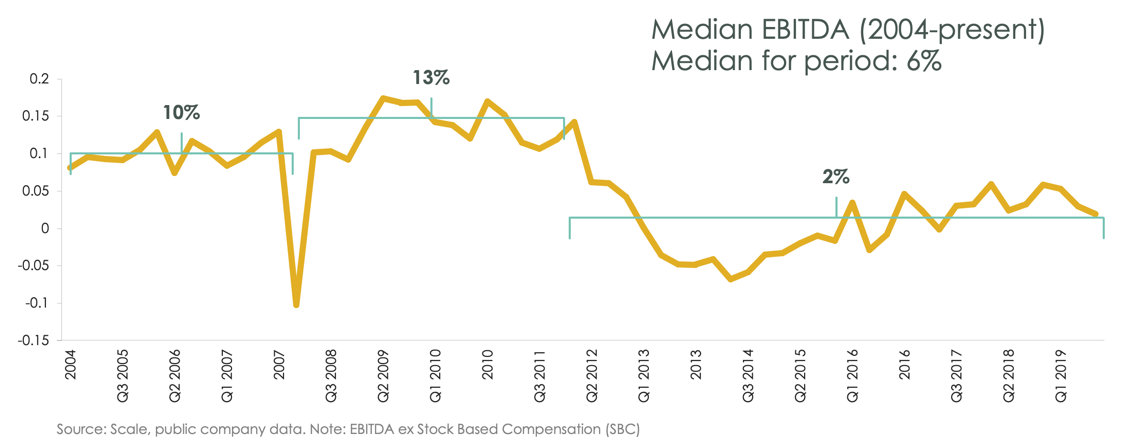
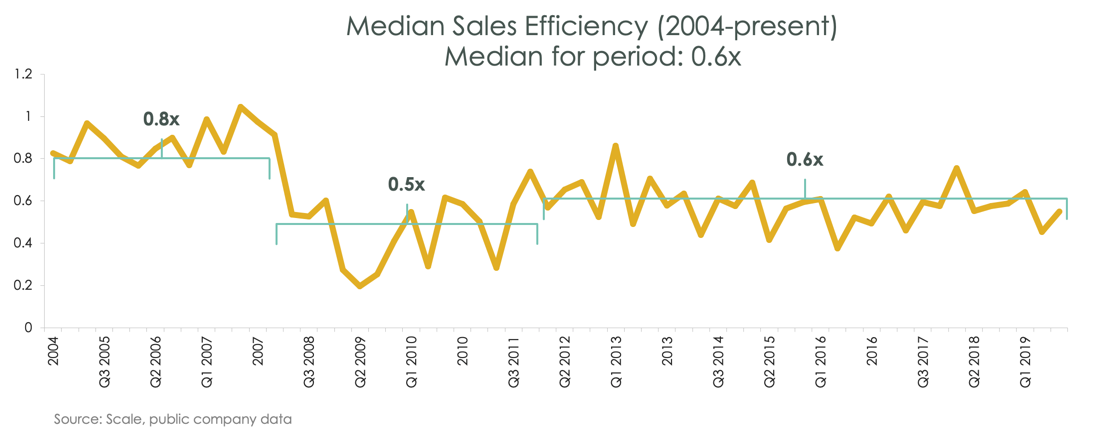
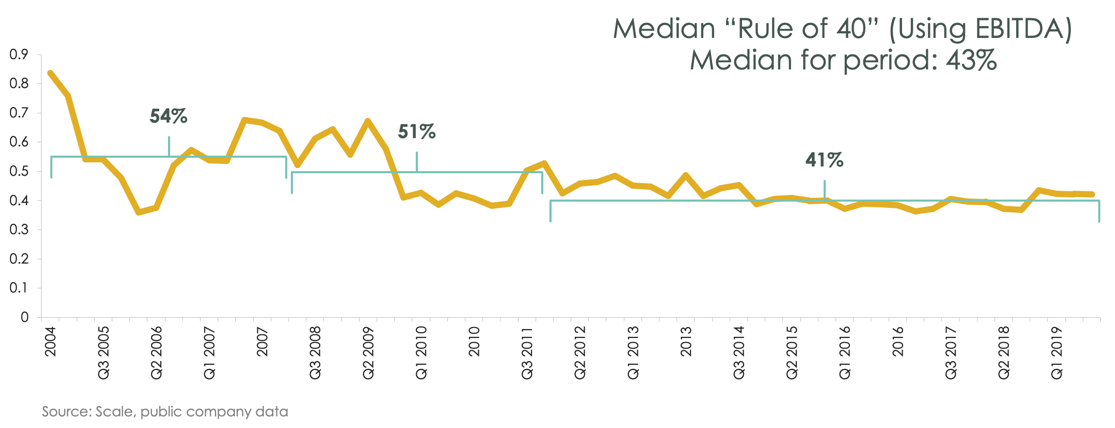
The short answer is no. The four charts below show growth rate, profitability, Sales Efficiency and the Rule of 40 (a combination of growth and profitability) for the entire public SaaS universe from 2004 to today. Each chart also shows separately the median for three sub-periods within this time period: pre-crash (2004 to 2008), the crash period (2009 to 2011), and post-crash (2011 to today).
The story is the same in every case. Pre-crash operating performance was stellar in what was then a new uncrowded market. The crash was brutal on growth and forced companies to get profitable fast. But since 2011, growth rates, EBITDA, Sales Efficiency and Rule of 40 measures have all been roughly flat and provide no justification for almost a doubling of valuations in the last two years.
So why are these companies trading so richly?
It’s all about the growth
Sometimes the answer is in plain sight. The big picture in all the above numbers is that public companies in this sector have been growing at 30% plus for 15 years now, since the Salesforce IPO in 2004. Growth has not gone up but, far more importantly, it has not gone down.
The SaaS gold rush will become the ‘Hunger Games’
Source: Microsoft
Microsoft posted quarterly results today that were well ahead of analysts’ expectations, but Azure’s growth rate continues to decline as it competes with AWS.
The company’s revenue for the first quarter of the fiscal year rose 14% year-over-year to $33.1 billion. Net income increased 21% to $10.7 billion, or $1.38 per share.
Revenue from Microsoft’s Productivity and Business Processes segment, which includes its Office products and LinkedIn, grew 13% to $11.1 billion. LinkedIn’s revenue increased by 25%.
Meanwhile, its Intelligent Cloud segment’s revenue increased 27% to $10.8 billion, with revenue from server products and cloud services growing 30%. The company said Azure’s revenue grew by 59%, but that represents a decline in growth rate that began a year ago, when Azure clocked quarterly growth of 76%. The rate has fallen more since then, with today’s report representing a drop from the 64% growth reported in the previous quarter.
Revenue from Microsoft’s personal computing segment grew 4% to $11.1 billion.
The company said it expects second-quarter revenue to be in the range of $35.15 billion to $35.95 billion.
Microsoft reports a strong fiscal first quarter, but Azure’s growth rate continues to decline